All Categories
Featured
Table of Contents
To asses danger Waydev allows you to determine how likely it is a particular commit will trigger issues. In this case, there are particular data points that you must consider, such as the devote's size, how far do the changes spread, as well as the modifications' depth. Continuous Combination (CI) and Continous Development (CD) are vital in today's engineering community due to the fact that they make sure that your team delivers software application in an iterative form.
Proven Methods to Control Cloud Costs
Our service immediately gathers information from the Continuous Combination and Continous Development pipelines and tracks Gitlab repos, enabling you to evaluate information without requiring any kind of manual input. This is an outstanding method to keep an eye on DevOps performance by concentrating on DORA metrics. By automating these processes and measurements, you might have a clear view of how implementation is going, evaluate what effects burn-down rates, what triggers traffic jams, and how to solve them.
With Waydev's Task Expenses report, you have consistent insights on how work is progressing and how things look economically. This enables you to reallocate resources to ship on time or enhance costs and communicate task status to company leaders. When done right, the aligns service requirements with innovation procedures, making it possible for Engineering Managers to enhance performance and analyze threats.
IT governance focuses on setting tactical instructions, policies, and oversight. Training should cover framework principles, new policies and treatments, governance roles and duties, and any governance tools or systems being executed.

Proven Methods for Reducing Cloud Spend in 2026
Threat management identifies dangers, assesses effects, and develops mitigation strategies. It makes sure governance properly addresses information security, disaster recovery, and regulatory compliance.
IT governance manages governance and dangers while preserving compliance with industry and government policies. Enhancing IT governance needs the right mix of IT financial investments, policy and personnel.
As companies increase their IT investments, the significance of a strong IT governance policy boosts. Chief info officers (CIOs) drive IT governance strategy along with other crucial stakeholders in the C-suite.
Maximizing Enterprise Performance Metrics Through Enhanced GovernanceEffective IT governance lines up innovation decisions with organization technique, controls risk, and guarantees IT resources are utilized effectively. This guide covers each step in useful detail, along with the frameworks, tools, and finest practices IT leaders utilize today.
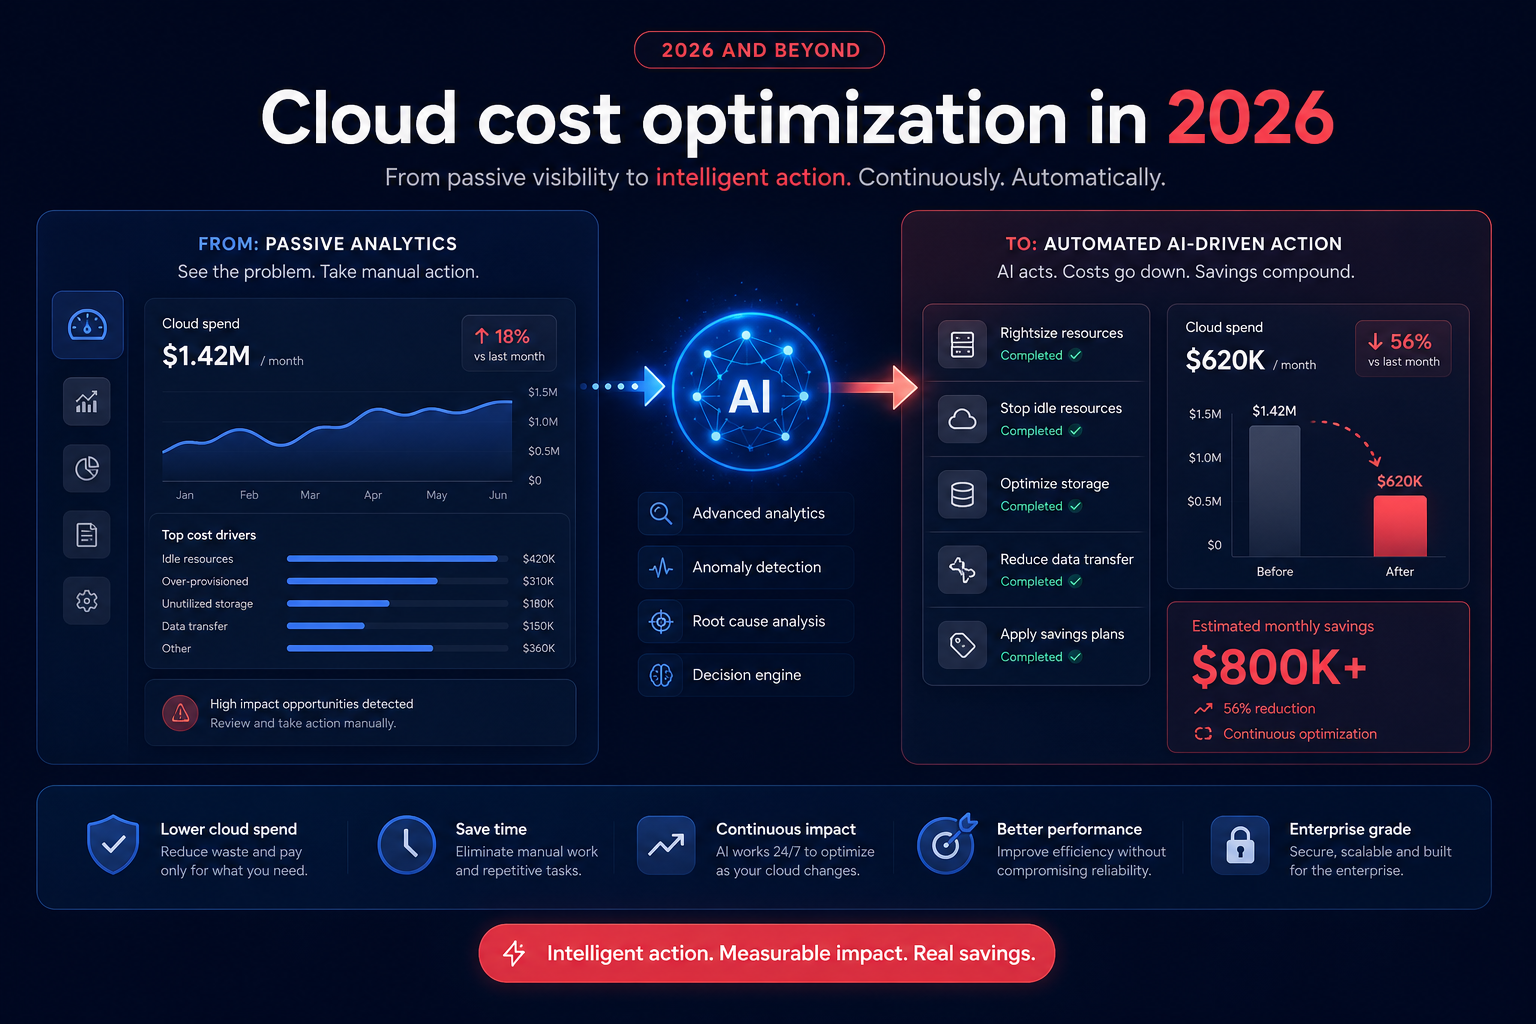
Improving Cloud Resource Management Best Practices
Assign clear accountability for each governance domain. Framework Primary focus Finest matched for IT governance and management, threat control, audit readiness Big business, controlled markets IT service management aligned to service needs Organizations with a mature IT service function International standards for IT service management and corporate IT governance Organizations looking for certified, worldwide recognized governance CMMI(Capability Maturity Model Integration)Process improvement rated on a scale of 1 to 5 Organizations benchmarking and improving development or delivery capability COSO (Committee of Sponsoring Organizations of the Treadway Commission)Internal control and business risk management Organizations focusing on financial controls and fraud deterrence CIS( Center for Web Security)Controls Cybersecurity and facilities strength Organizations enhancing technical security posture Numerous organizations integrate frameworks. Governance that is not determined does not improve.

Latest Posts
How Cloud Optimization Redefines 2026 IT Infrastructure
Establishing Robust Cost Frameworks
Proven Tactics to Control Enterprise Costs